Operations | Monitoring | ITSM | DevOps | Cloud

How to Build a Successful SIEM Migration Strategy

At least once a week, a team reaches out to discuss migrating from an established SIEM or analysis platform. This major decision is influenced by several compelling factors, which can create significant work for engineering teams and pose risks to the business. The cost of switching to a new platform, often referred to as displacement costs, can be substantial.

Everything You Need to Know About SIEM Logs

That moment when your production system goes down, and you're stuck piecing together logs from twenty different services? It’s frustrating and slow—especially when you need answers fast. SIEM logs help bring order to this chaos, giving you a structured way to track security events and system activity. But understanding how to use them effectively isn’t always straightforward, and most documentation can feel more complicated than the problem itself.

Everything You Need to Know About Microsoft Sentinel Pricing

Keeping your organization secure is more important than ever. Microsoft Sentinel, a cloud-native Security Information and Event Management (SIEM) solution, helps detect and respond to threats effectively. But to get the most out of it, it’s important to understand how the pricing works.

Building Next-Generation SIEM Operations for Enterprise Security

Cybersecurity today is not just about defending against attacks. It’s about proactively managing risks in a landscape where threats are growing in volume and sophistication. With data volumes rising by 30% in just the past year and the average cost of a data breach now exceeding $4 million, traditional Security Information and Event Management (SIEM) systems are no longer enough.
Sponsored Post

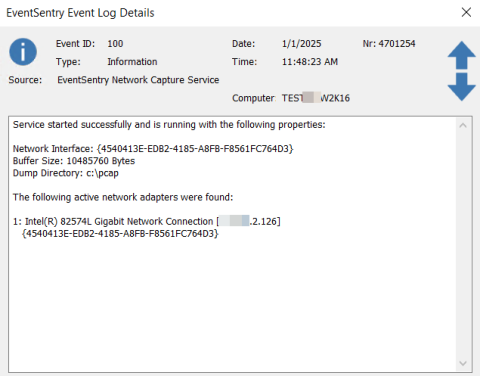
Capturing Network Traffic anytime

Capturing network traffic is usually done either for security reasons or to troubleshoot networking issues. But by the time you initiate a network capture (either manually or automatically) it’s often too late already – the train has already left the station. Point in case: Say your SIEM (obviously EventSentry) detects abnormal or suspicious behavior in a log and a network capture is initiated.

Cribl and CrowdStrike Partner to Transform Data Management for SIEM Solutions

Cybersecurity is moving fast, and if your security data management strategy can’t keep up with your growth, you’re already behind. Security operations centers (SOCs) today face mountains of data spread across countless tools and platforms. Combine that with evolving cyber threats, and you have an environment that demands a smarter approach to SIEM data management.