Operations | Monitoring | ITSM | DevOps | Cloud

How a Solutions Architect Brought Multi-Cloud Migration to OpenSearch | Tony Piazza

Aiven Senior Solutions Architect Tony Piazza joined the company in March. Within months he had merged five PRs adding Google Cloud support and Terraform-based provisioning to the OpenSearch Migration Assistant, a tool that previously only worked on AWS. Tony talks with Jay Miller about: Why he went from consulting to open source contribution. How a consultant’s habit of finding project risks early shaped the work. His first conference keynote at OpenSearchCon. What contributing as a vendor-neutral company looks like. Where he’s contributing next, including ML Commons, Data Prepper and the docs.
How to Integrate NinjaOne with a SIEM

In this episode of NinjaOne01, Jeff Hunter, Field CTO at NinjaOne, walks through NinjaOne’s new SIEM Exporter App. The app is a dedicated place to set up and monitor the webhooks that send NinjaOne activity data to your third-party SIEM (Security Information & Event Management) system. Note: this is an early access feature, so contact your account manager to have it enabled for your account. What this video covers.

Why AI SRE Agents Need More Than Observability Data with Groundcover | Civo Navigate London

Your AI agent can read every log, metric and trace in seconds. It still can't tell you why things broke. At Civo Navigate London, James Herbert of groundcover explains why AI SRE agents need that context to travel the whole development lifecycle. He shows how agents embedded in the tools where software is built and run can move from isolated tasks to investigating and acting with the full picture.

7 Layers of Agent Security (1 in 6 repos has leaked credentials)

I scanned 10,705 public GitHub repos for leaked credentials. After removing obvious placeholders, 3,543 still had something that looked like a key, and 1,680 held almost 7,000 credentials in recognizable formats like Stripe keys. If you're new to coding with agents (or you've been a dev for decades), this is the setup I'd want you to have before you ship anything public.

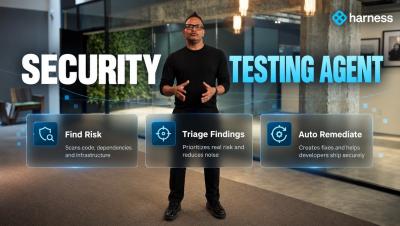
AI Finds and Fixes Security Vulnerabilities | Harness Demo

What if AI could find a security vulnerability, determine whether it actually matters, write the fix, validate it, and open a pull request for review? In this demo, see how Harness Security Testing Agents work together to move from vulnerability detection to a verified fix with an audit trail along the way. The system uses three agents: Harness can analyze where vulnerabilities exist in your environment, determine whether they’re actually reachable, prioritize what needs to be fixed, and automatically create remediation pull requests.

Searching Sentry Logs with Regex

We use Sentry's new Regex search for Logs to hunt for non-obvious bugs in our app. What do you do when traces show that Postgres jobs are backing up? Logs are trace-connected, so by looking at one of the affected traces, we can see all of the logs on that trace. In there, we can see Postgres has logged that it acquired a lock only after a long wait. Using regex, we can find all of these logs that describe acquiring a lock after a 10-second-plus wait. That narrows our search from thousands or hundreds of logs down to about a dozen.

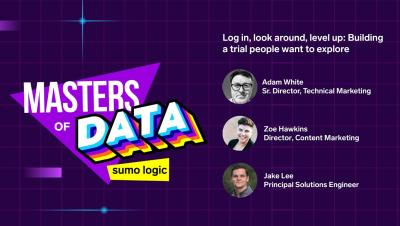
Log in, look around, level up: Building a trial people want to explore

We turned the mic around for this episode, with Zoe Hawkins interviewing Adam White and Jake Lee about Sumo Logic’s redesigned free trial. The new 14-day sandbox comes preloaded with realistic data feeds, Cloud SIEM, and our AI agents, so no one has to build collectors or open tickets before finding out whether the platform fits. Adam and Jake walk through the guided “choose your own adventure” paths, the broad, open-ended questions that bring out the best in Mobot, and how the trial will keep pace with new releases.

We Ran Minecraft on 4 Raspberry Pis with Kubernetes and Monitored it with Open Source

Why did we do this? Not important: jump to 1:31 to see the Pis. TL;DR: We stuck Minecraft on kubernetes running on 4 Raspberry Pis in a 3D-Printed case, and monitored it with open source observability. Huge thanks to Percona DBA Ivan Zaitsev for putting the demo together for Percona University, Montevideo. Coroot automatically collects and visualizes all your telemetry data: logs, metrics, traces, profiles, and a complete map of your services. With the complete context of eBPF, it can diagnose the exact cause of an incident in seconds, and show you the exact commands to fix it.