It feels like a lifetime ago, well, 3 years is a lifetime in tech, that I wrote a blog post explaining how we rewrote our API server from Golang to Ruby on Rails. Here we are and I'm about to explain about how we've been back and forth doing the same thing for our CLI. Just after that time, I wrote the first version of our CLI utility in Golang. However, with only me knowing Golang on the team, we weren't able to achieve the velocity and pace of adding features within the CLI as I'd like.
When you're evaluating a language for your next project, few things are more important than available third-party libraries and the package manager that ties them together. While early versions of Go lacked a package manager, they've made up for lost time. In this article, Ayooluwa Isaiah introduces us to go's module ecosystem to help us decide if go is "a go" for our next project.
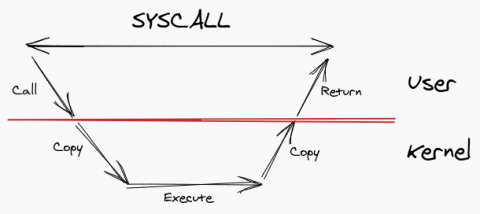
In Linux, system calls (syscalls) are at the heart of everything. They are the primary interface through which an application interacts with the kernel. Therefore, it is vital that they are fast. And especially in a post-Spectre/Meltdown world, this is all the more important.
With a near-endless list of Go Modules, it can be overwhelming trying to decide which is best for your Go build. For new Go developers, it can be difficult to pick a winner for your specific use case. This phenomenon is nothing new. In fact, it’s one of the reasons why open-source is so important for developers. Oftentimes, when a module is published by a developer, it was likely developed to solve a specific problem that they are facing.
Go Module vulnerabilities frustrate the lives of many Go developers and can turn a simple project into a battle of endurance between the dev and their patience. With the process of CI/CD shifting left more and more, it’s becoming even more pertinent for developers to be able to track and report vulnerabilities as early as possible. JFrog GoCenter can help track and mitigate vulnerabilities and make the lives of Go developers easier.
If you’re a Golang developer using Visual Studio Code, keeping at-risk Go Modules out of your apps just got easier, and for free. Today we’re announcing a new version of the JFrog extension for VS Code, available for free download. This integration brings live vulnerability information about every public Go Module you’re using directly into your source editor from the rich metadata of JFrog GoCenter.