
Operations | Monitoring | ITSM | DevOps | Cloud

Restoring Compliance After Missed SAP Patch Cycles

Avantra restores SAP compliance after missed patch cycles by measuring the real gap on every system, automating the catch-up in risk order, and monitoring continuously afterward. A missed cycle can leave SAP operations out of compliance or exposed to documented vulnerabilities, and until each system is assessed, the impact is unknown. Getting “back to good” requires three steps: The patching itself is rarely the hard part.
ISO 27001 Compliance: What Auditors Require and When You Need the Certificate

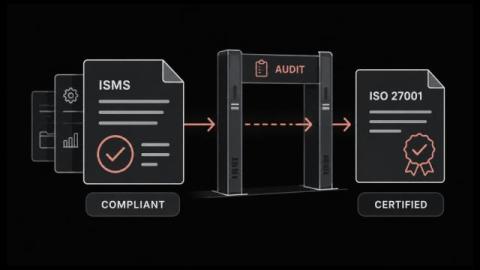
ISO 27001 compliance means running your information security the way ISO/IEC 27001 sets out. Most teams meet the standard when a customer sends over a security questionnaire. It lands as one more line on a cybersecurity compliance checklist. That framing hides the decision underneath it. You can follow the standard without ever being certified against it. The two routes cost very different amounts. In this blog, you will: You will finish able to decide whether you need the certificate, and what it takes.

Agentic AI or CLM Compliance? A Buying Test for Financial Services

Consider a hypothetical bank negotiating a technology supplier agreement. An AI agent spots a change to the audit-rights clause, proposes replacement language and prepares the contract for approval. The review looks faster. Then someone asks which policy version the agent used, whether the replacement was approved, and what prevents the unsigned draft from becoming the operational record. Those questions should shape the buying decision.

How Federal IT Teams Move to FIPS 140-3 Without Disrupting Authorization or Service Continuity

A credible FIPS 140-3 transition does more than replace an operating system. It protects authorization timelines, service continuity, rollback options, and accountability across the operational boundary.

What Is DORA Compliance? The Digital Operational Resilience Act Explained

The Digital Operational Resilience Act has applied to EU financial firms since 17 January 2025. The first year was mostly paperwork. In year two, supervisors want proof, and most of that proof sits with IT operations. DORA joins the other rules on your cybersecurity compliance list, with much tighter clocks. A major incident needs its first report within 4 hours of classification. In this blog, you will: By the end, you will know what DORA compliance asks of your IT team and where to begin.

From SOCI Compliance to Continuous Infrastructure: How Puppet Helps Protect Critical Infrastructure

Australia’s critical infrastructure landscape has changed significantly. The Security of Critical Infrastructure Act 2018 (SOCI Act) has evolved from a framework focused primarily on identifying critical assets and reporting incidents into a broader risk-management and operational-resilience regime. The 2024 reforms reinforced that direction, increasing the focus on the systems, data, and technology dependencies that underpin Australia’s essential services.

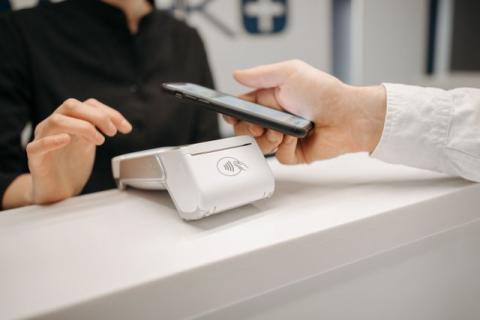
Digital ID Arrives at the Till: What the Alcohol Rule Change Means for Checkout Integrations

For years, proof of age at an alcohol till in England and Wales meant something you could hold in your hand: a passport, a photocard driving licence, a PASS card. That's no longer the whole list. Since mid-September 2026, licensed premises can accept certified digital proof of age from a customer's phone.

Compliance guardrails for regulated delivery

One multinational running on Upsun operates more than 400 websites. Each subsidiary has its own sites, its own team, its own release schedule, and its own local requirements. What they share is one infrastructure control layer: the same access model, the same encryption defaults, the same activity records, the same region and backup policy on every project. Adding the 401st site does not add a 401st set of infrastructure controls for someone to review.

ISO 20000 Certification: Prerequisites, Process, and Cost

ISO 20000 certification means two different things depending on who is asking. One is an audit of your organization against ISO 20000. The other is an exam that one person sits. Search results mix the two together, and teams lose weeks to it. A service desk manager hunting a company certificate lands on a training catalog. They book a course nobody needed. In this blog, you will: You will finish able to scope the project and brief a certification body.

ISO 20000 in ITSM: What the Standard Actually Requires From Your Service Desk

Certification against ISO 20000 puts your service desk under audit. That audit runs on what your team wrote down at the time. The standard does not care how your team describes its process. It does not care which ITIL 4 practices you adopted. It cares what your records show, so auditors spend their time in your tickets, approvals, and review minutes. In this blog, you will: You will finish knowing which of your records would survive an audit.