
Operations | Monitoring | ITSM | DevOps | Cloud

Security KPI Dashboards for SAP Operations Teams

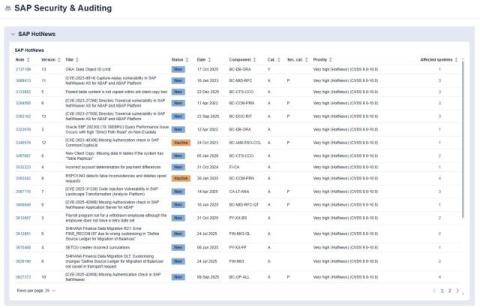
An Avantra SAP security dashboard gives SAP operations teams one view of SAP security KPIs, covering SAP Notes and HotNews status, system hardening, user access risk, and audit compliance across on-premises, hyperscaler, and RISE with SAP systems. Security teams have their own tools: a SIEM, a SOC console, vulnerability scanners. SAP operations teams usually don’t.
Sponsored Post

From Zero to Managed in Record Time

If you've spent any time in the SAP ecosystem, you know the "Configuration Tax." It's that invisible, compounding fee paid in hours, manual effort, and caffeine. SAP teams pay tax every time new systems or integrations are brought under observability and management. For years, the industry accepted that observability required a heavy initial lift. Changes in monitoring policy or underlying infrastructure triggered additional effort often parallel and size and scope to initial onboarding.
Sponsored Post

Collective IQ Business: meet the artificial intelligence that transforms IT management

The employee digital experience (DEX) is no longer just a concept; it has become a concrete discipline supported by specialized tools. At the center of this transformation is Collective IQ, Almaden's DEX solution, available in the Essential and Business editions. The Business edition includes AlmaAI a family of generative AI capabilities that take IT management to a new level. These capabilities allow IT administrators to simplify their analysis and faultdetection processes, providing everything from daily prioritization to predictive analytics and naturallanguage interaction.

Models Are Getting Really Good At Git

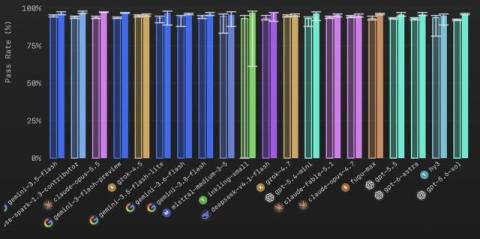
I built GitBench because I was curious about how well models did git things. It turns out that it was a good idea because some models will surprise you. Some of the frontier models were remarkably bad and some cheap open models punched above their weight class. But, as they say, “the times they are a changin’”. Before I go too deep into the latest results, you may want to read up on GitBench and what it is and why I built it in the previous blog post.

EU AI Act 2026: delay, new deadlines & article 73 reporting

On July 27, 2026, the Digital Omnibus on AI, Regulation (EU) 2026/1744, entered into force and rewrote the EU AI Act's timeline. The high-risk obligations that were due to apply on August 2, 2026, including Article 73 serious-incident reporting, now apply from December 2, 2027 for standalone high-risk systems (Annex III) and August 2, 2028 for AI embedded in regulated products (Annex I). Not everything moved.

What Is DORA Compliance? The Digital Operational Resilience Act Explained

The Digital Operational Resilience Act has applied to EU financial firms since 17 January 2025. The first year was mostly paperwork. In year two, supervisors want proof, and most of that proof sits with IT operations. DORA joins the other rules on your cybersecurity compliance list, with much tighter clocks. A major incident needs its first report within 4 hours of classification. In this blog, you will: By the end, you will know what DORA compliance asks of your IT team and where to begin.

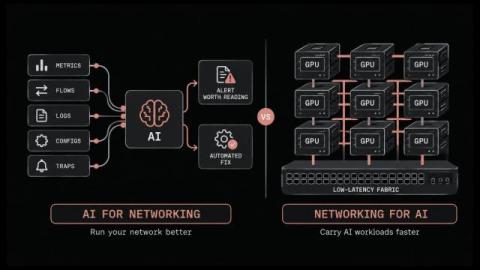
What Is AI Networking? The Two Pillars and Which One You Need

AI networking means two different things. Vendors rarely say which one they are selling. One is using AI to run the network you already have. The other is building network infrastructure fast enough to train AI models. Both pillars are real, and they solve completely different problems. Most network teams only ever need the first. In this blog, you will: You will finish knowing which pillar your own question belongs to.