Operations | Monitoring | ITSM | DevOps | Cloud

The latest News and Information on CyberSecurity for Applications, Services and Infrastructure, and related technologies.

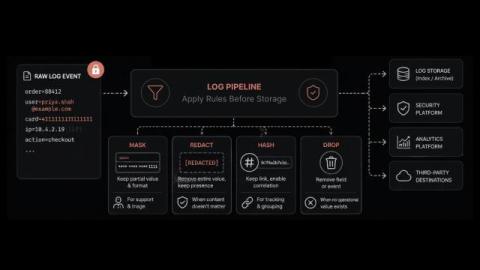
PII Redaction in Logs: Mask, Redact, Hash, or Drop?

Sensitive values reach your logs without anyone deciding they should. A debug line prints a whole request object. An error message carries the query string. A customer email address is suddenly stored in three systems. PII redaction in logs then gets treated as one setting to switch on. In practice it covers four separate treatments. The value is already inside the message before log ingestion finishes. In this blog, you will: By the end you can write a rule for each field and defend it.
Outrun the Threat Window: AI-accelerated Vulnerability and Patch Management

The gap between vulnerability disclosure and active exploitation is shrinking—often from weeks to mere hours. Traditional patching cycles no longer cut it. In this session, discover how AI-accelerated solutions can help you: Identify exposed assets faster Prioritize vulnerabilities by real-world risk Remediate across Windows, macOS, Linux, and hundreds of apps Verify success with a connected workflow Learn how our approach, powered by AI-driven insights and automation, can help you close the gap before attackers strike. Watch now and take control of your patch management.

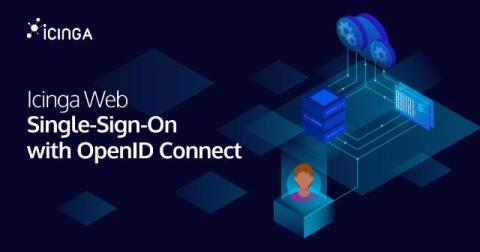
Icinga Web SSO walkthrough

The ability to log into all corporate applications with one username and password is pretty convenient, even compared to a password manager. As a benefit, the IT department can centrally enforce one desired two-factor auth mechanism. Now we, Icinga, also provide a so-called OpenID Connect integration for single sign-on. By the end of this text you’ll know how to connect your Icinga Web instance to the ID provider of your choice.

When login systems become an ops problem

SSO usually enters a company as a convenience project. People are tired of juggling passwords, new employees need access faster, and security wants fewer loose credentials floating around the business. At first, that sounds like a clean IT improvement. Then the company grows, tools multiply, teams work across more environments, and login becomes part of the operating layer that keeps the whole business moving.

How we made vulnerability fixes review-ready with Agentic Pipelines

Routine vulnerability fixes are rarely difficult in isolation. The interruption that they cause is the problem: pick up the ticket, trace the dependency, update the package or image, regenerate files, run the checks, open the pull request, then return after deployment to close the loop. That repeated handoff was a good candidate for automation with agentic pipelines. The goal was simple: start the day with a tested pull request instead of another ticket to pick up.

The big question at Black Hat USA 2026: "how do I know?"

Black Hat USA 2026 brought more than 20,000 people to Mandalay Bay in Las Vegas. We were there as a Platinum sponsor at booth 4208, and across two days on the business hall floor we had more than 750 conversations with security engineers and architects. Almost every one of them, whatever it started as, turned into a version of the same question: how do I know? How do I know whether a vendor's AI does what the banner says? How do I know what my agents are doing on the network?

Introducing APEX: Adversarial Pattern Extraction and Correlation

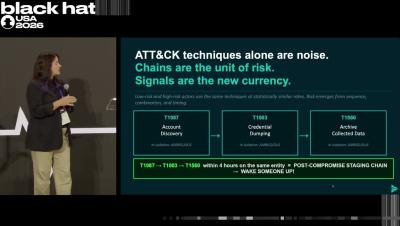
In this Black Hat talk, Nicole Beckwith introduces APEX (Adversarial Pattern Extraction and Correlation), a detection framework—not a Cribl product—that clusters TTP-based signals around entities to support behavioral detection. It is intended for security practitioners, SOC and detection teams, and threat hunters who want to learn how to use raw telemetry or OCSF data, TTP chaining, time windows, criticality, and cross-correlation to detect behavior beyond static indicators and rule-count coverage.

The Strategic Value of Emergency Readiness: Safeguard Operations and Human Capital

Emergency readiness often gets seen as just another compliance task - a checklist of fire extinguishers and evacuation routes to tick off. But that view misses the bigger picture. Real readiness isn't a static obligation; it's a dynamic strategy that protects your entire operation. It safeguards your financial stability, keeps things running smoothly, and, most importantly, shows you care about your people.

Phishing vs. Smishing vs. Vishing vs. Quishing: What's the Difference?

Ask people in the same company to define phishing, and the answers may drift. At least one will use the word as a catch-all for anything suspicious that reaches an inbox, and someone else will apply it to a phone call. That drift can have operational consequences. A ticket labeled phishing that was actually a spoofed call to the help desk may be routed to the wrong queue, trigger an inappropriate playbook, or distort the metrics used to plan future controls.

The Safest Place to Run an AI Agent Is On a Cluster That Doesn't Trust It

Every organization running AI agents has already made a hosting decision. Most made it by accident. The sales team switched on the agent built into their CRM. Engineering is piloting a coding agent in a vendor’s cloud. Someone on the data team deployed a LangGraph service to a VM with a database key in an environment variable, and someone else is running an agent framework on a laptop with production credentials in a dotfile. Each of these is a hosting decision.