
Operations | Monitoring | ITSM | DevOps | Cloud

How Pharmacies Can Streamline Call-In Prescription Workflows With OnPage

Pharmacists manage much more than dispensing medications. Throughout the day, they may be processing prescriptions, communicating with healthcare providers, assisting patients and coordinating with other pharmacy staff, all while managing a steady flow of incoming calls. For pharmacies that accept prescriptions by phone, those calls add another important communication workflow to an already busy environment.
Meet Ada - AI Assistant: Ask the Question, Approve the Change

Ask any operations team what question comes up most, and it isn’t about alert routing or escalation logic. It’s the one typed into a channel a dozen times a day: who’s on call for this right now? It’s also one of the slowest questions to answer. The schedule is set up correctly, the overrides are in place, and the group’s ownership is right.

ilert now supports a native Bleemeo integration

Bleemeo monitoring now connects natively to ilert, linking threshold detection to on-call management and alerting. DevOps, SRE, and IT operations teams get a direct path from a breached threshold to the phone of the engineer who can fix it, and back to a clean slate once the problem is gone.

How to Send Critical Alerts to the OnPage App | 3 Ways

What are the different ways to send a critical alert to the OnPage app? This video shows three ways people and external systems can trigger a high-priority OnPage mobile alert that's also HIPAA compliant (secure or healthcare use cases): These options are particularly useful for users with OnPage mobile licenses who do not have a Silver or Gold plan.

On-Call Alerting vs. Mass Notification: What's the Difference?

When an urgent situation occurs, organizations need more than a way to send a message. They need a communication strategy that considers who needs to receive the message, whether they need to take action and how quickly they need to respond. This is where the difference between on-call alerting and mass notification becomes important. A critical IT incident, for example, may require an immediate response from a specific on-call engineer or incident response team.

Grafana Alerting: Scale alert routing without scaling complexity using multiple notification policies

Alert routing often starts simple. A team creates a few contact points, adds some label matchers, and builds a notification policy tree that sends each alert to the right destination. But alerting configurations rarely stay simple. As an organization grows, its notification policy tree must accommodate more teams, services, and routing requirements. Changes for one team still require editing a global configuration, making ownership less clear and independent provisioning harder.

New Alerts module, smarter workflows, AI-powered assistance, and more!

In this edition of ServiceDesk Plus Premiere, our product experts take you through the latest updates across both ServiceDesk Plus Cloud and On-Premises, with enhancements designed to make everyday IT service management more efficient. For ServiceDesk Plus Cloud, we’ll explore the new Alerts module, enhanced criteria-based workflow routing, Resolution Assist powered by similar resolved requests, and asset discovery enhancements that bring greater visibility into the security components of Windows assets.

How to Configure Redundancy Channels in the OnPage Console

Learn how to configure redundancy notifications and copy recipients for a contact in the OnPage Console. This video walks through disabling Secure Messaging, setting the redundancy time interval, selecting additional delivery channels and sending message copies through email, SMS or IVR/voice call. Important: Disabling Secure Messaging means messages will no longer be delivered through OnPage’s secure channel. This configuration is not HIPAA compliant and should not be used for healthcare communications requiring HIPAA compliance.

From alert to resolution: Manage incidents with Bits Chat in Slack

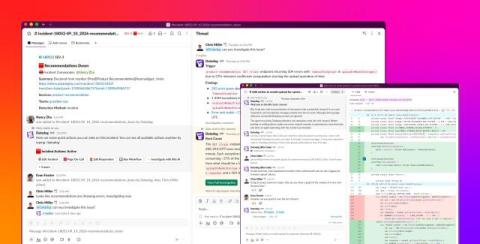
When an issue in production triggers an alert, the people responding to it are often working in Slack while the evidence they need is elsewhere. Responders need to move between conversations, telemetry data, source code, and incident tooling as they form hypotheses, coordinate actions, and keep stakeholders informed. That context switching can slow down a time-sensitive investigation and make updates harder to follow.

ilert AI SRE is generally available

When you get paged at 3am, it takes about 30 seconds for the notification to reach you and maybe two minutes until you're in front of a laptop, awake enough to read. What you see then is usually a raw alert. A metric name, a threshold, a link to a dashboard. Then the ritual starts: open the dashboard, check what deployed in the last few hours, grep the logs for the first error, ask in Slack whether anyone touched the database. ‍ Most of that time is search.