Operations | Monitoring | ITSM | DevOps | Cloud

CRA turns software trust from assumed to legally required

For years, buying software meant trusting the vendor. The Cyber Resilience Act changes that relationship by codifying what vendors must do – auditing dependencies, confirming exploitable vulnerabilities, and enforcing security best practices – as legal obligations, not internal choices. For customers, that means software safety is no longer a matter of brand reputation. For vendors, it means governance gaps that were once internal concerns are now deal blockers.
On Release Days We Wear Teal Episode for release 4.19

In this episode, Leon explores some of the new features, functions, updates, and improvements in release 4.19, which includes a raft of AI-enabled features including the Cribl Apps, integrated MCP server, and the fact that AI features are now turned on by default. For more information, check out these links.

I'll have my AI agent call your AI agent: Battle for your digital hub

On this episode of Masters of Data, we unpack what it actually means to expect AI to be the primary interface for everything we do. We dig into the pull toward centralizing work in a single hub like Claude versus staying spread across specialized tools like Slack, Asana and Zoom, and where the line sits between helpful automation and letting an agent speak on your behalf. We also get into the "chief of staff" agent workflow for daily roundups and why specialized, best-of-breed tools aren't going anywhere, even as hubs get smarter.

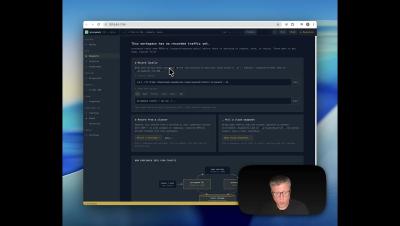
Instant Kubernetes Observability with Proxymock #speedscale #kubernetes #ebpf #devops #cloudnative

Learn how to get instant observability into your Kubernetes cluster by installing the Speedscale operator and proxymock tool. In this step-by-step tutorial, we walk you through setting up the operator to capture live network traffic (including encrypted traffic, API calls, and database calls) without complex instrumentation or manual configuration.

Scanners aren't enough. Here's the layer most teams are missing.

Vulnerability scanners tell you what's wrong with what you already pulled. They don't stop a malicious package from entering your environment in the first place. A private registry with minimum release age policies adds that missing layer – packages newer than two or three days don't reach developers until the industry has had time to identify and remove malicious ones from public registries. Active campaigns like TeamPCP are targeting npm, PyPI, and Maven Central right now. The gate has to come before the scan. Cloudsmith provides that gate.

The Lonely Journey (and How to Find Your Fellowship)

Coming into IT leadership can be a drastic change, with a multitude of different responsibilities, new skills to learn, and a whole organization looking to you to make decisions on the kind of technology that will keep them running. Unfortunately, it also means that even though you’re the most connected person in the company, you can also be the loneliest. IT leaders face unique issues that other leaders in the organization don’t.