
Operations | Monitoring | ITSM | DevOps | Cloud

The latest News and Information on Containers, Kubernetes, Docker and related technologies.

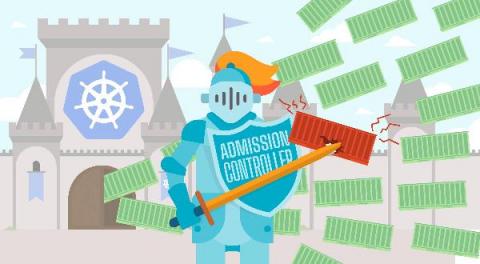
Kubernetes admission controllers in 5 minutes

Admission controllers are a powerful Kubernetes-native feature that helps you define and customize what is allowed to run on your cluster. As watchdogs, they can control what’s going into your cluster. They can manage deployments requesting too many resources, enforce pod security policies, and even block vulnerable images from being deployed. In this article, you’ll learn what admission controllers are in Kubernetes and how their webhooks can be used to implement image scanning.
Shielding your Kubernetes runtime with image scanning and the Sysdig Admission Controller

Implementing image scanning on a Kubernetes admission controller is an interesting strategy to apply policies that need Kubernetes context, and create a last line of defense for your cluster. You are probably following the image scanning best practices already, detecting vulnerabilities and misconfigurations before they can be exploited. However, not everything you deploy goes through your CI/CD pipeline or known registries. There are also third-party images and, sometimes, manual deploys.

How to monitor Amazon ECS with Elastic Observability

With an increasing number of organizations migrating their applications and workloads to containers, the ability to monitor and track container health and usage is more critical than ever. Many teams are already using the Metricbeat docker module to collect Docker container monitoring data so it can be stored and analyzed in Elasticsearch for further analysis. But what happens when users are using Amazon Elastic Container Service (Amazon ECS)? Can Metricbeat still be used to monitor Amazon ECS? Yes!

The Coralogix Operator: A Tale of ZIO and Kubernetes

As our customers scale and utilize Coralogix for more teams and use cases, we decided to make their lives easier and allow them to set up their Coralogix account using declarative, infrastructure-as-code techniques. In addition to setting up Log Parsing Rules and Alerts through the Coralogix user interface and REST API, Coralogix users are now able to use modern, cloud-native infrastructure provisioning platforms.

Industry-First Pay-as-you-go SaaS Platform for Kubernetes Security and Observability

We are excited to introduce Calico Cloud, a pay-as-you-go SaaS platform for Kubernetes security and observability. With Calico Cloud, users only pay for services consumed and are billed monthly, getting immediate value without upfront investment.

Splunking AWS ECS Part 1: Setting Up AWS And Splunk

It’s no secret that Amazon Web Services is a powerhouse Cloud provider, and one of the market pioneers in Cloud operations. They do, after all, power some of the world’s biggest and most modern systems we all use and love today. It’s natural then that they attract a lot of users both big and small to deliver high quality and effective solutions. With growing user demand comes the need for new methods of visibility and intelligence.

Monitoring Challenges Emerge as Agencies Embrace Container Technology

Container technology is catching on big-time in the federal government as agencies such as the USDA and the National Institutes of Health look to containers to simplify software development and reduce costs. Containers offer enormous advantages over traditional “waterfall” application development processes. A containerized approach makes it easier for developers to create and deploy software faster and with fewer errors.

Runtime security in Azure Kubernetes Service

Runtime security for Azure Kubernetes Service (AKS) environments requires putting controls in place to detect unexpected and malicious behavior across your applications, infrastructure, and cloud environment. Runtime threats include things like: Even if you’re taking advantage of tools like container image vulnerability scanning, Kubernetes pod security policies, and Kubernetes network policies with AKS, not every risk will be addressed.