Operations | Monitoring | ITSM | DevOps | Cloud

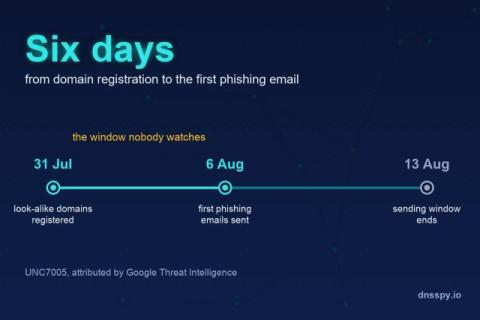
Six Days: What UNC7005 Shows About the Gap Between Domain Registration and Attack

On 20 August, Google Threat Intelligence published an analysis of a phishing cluster it tracks as UNC7005. Google assesses with moderate confidence that the cluster is connected to ICE RELIC, the Russian actor formerly tracked as APT29 and also known as Midnight Blizzard.
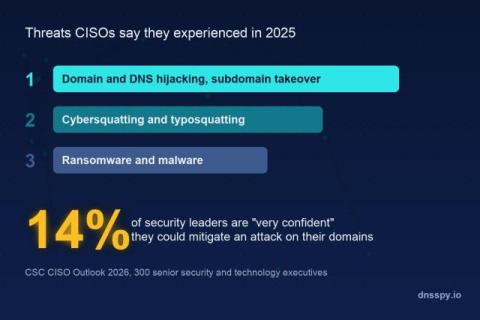
CISOs Now Rank Domain and DNS Hijacking Above Ransomware

CSC's CISO Outlook 2026 report surveyed 300 senior technology and cybersecurity executives in the first quarter of 2026, split evenly across North America, Europe and the UK, and Asia-Pacific. When asked which cyber threats they had actually experienced in 2025, not which ones worried them but which ones happened, the answer at the top of the list was domain and DNS hijacking, and subdomain takeover. Ahead of ransomware. Ahead of malware.

How Does a Domain Protect Critical IT Infrastructures?

A digital address routes traffic and anchors trust. The domain is far more than a convenient label that users type into a browser, since it carries out essential functions that keep critical systems connected, authenticated, and protected from harm. For organisations running mission-critical operations, it functions as a gatekeeper that determines whether legitimate users reach a service and whether attackers are turned away at the door.

Monitoring the Monitor: When One of Our Uptime Vendors Went Quiet for 27 Hours

DNS Check watches its own infrastructure with several layers of monitoring, including DNS Check itself and third-party uptime monitoring services. One of those vendors polls a private health endpoint on our servers every five minutes, from probes around the world. That endpoint runs a set of internal checks (disk space, mail delivery, background job queues, DNS resolvers, and more) and returns an error if any of them fail. If it errors or stops responding, the vendor alerts us.

DNS Monitoring: What to Track and Where to Watch It From

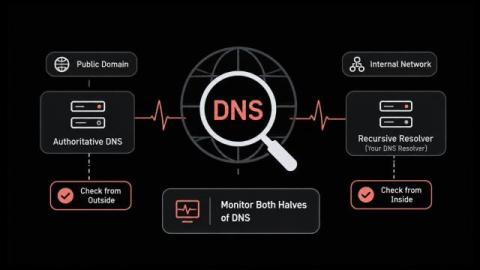
DNS monitoring asks your name servers the same question on a timer and checks the answer that comes back. Most teams aim it at their public domain and stop there. That covers half the problem. Your public domain and your internal resolver fail in different ways. A check from outside the building never sees the second one. In this blog, you'll see: By the end you'll know which half of your DNS nobody is watching. A DNS check sends a query and reads the reply. The reply can fail three ways.

What's taking DNS-PERSIST-01 so long?

In February, Let’s Encrypt announced that DNS-PERSIST-01 was coming, “some time in Q2 2026.” It’s October, and it’s nowhere close to ready. We’ve been waiting for DNS-PERSIST-01 since January, along with every other ACME client and lots of organizations. DNS-PERSIST-01 promised to simplify domain validation and make automation easier, but we had to wait on Let’s Encrypt. Let’s Encrypt is waiting on a redesign, a standards body, and maybe one more vote.

How to Fix Slow DNS Lookups Across Clients, Resolvers and Networks

Why does every page, login and business application hesitate before anything loads, even when bandwidth graphs look healthy? That pause usually comes from name resolution: no connection starts until its hostname has been translated into an IP address, and whatever time that translation takes is added to the request. Slow DNS seldom shows up as a clear error.