Operations | Monitoring | ITSM | DevOps | Cloud

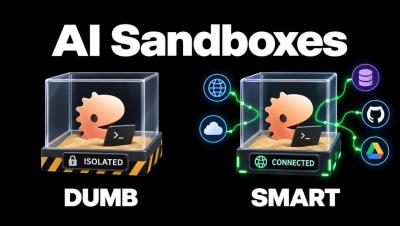
Stop Running Claude Code on Your Laptop: 2 Types of Agent Sandbox

Every week there's a new agent sandbox, and they all promise the same thing: a safe place for your agent to run code. In this video we split them into two types, dumb sandboxes and smart sandboxes, so you can sort any provider by what it can actually do instead of how it's marketed. You'll see where today's providers sit, why dumb sandboxes still have a real place, and how to pick the kind your agent's job needs.
Detection Workflows in Cribl Detect

Get a deep dive walk through of detection posture management and detection engineering workflows within Cribl Detect. See how Cribl Detect helps view current coverage with MITRE ATT&CK mappings, pinpoints detection and telemetry coverage gaps, proactively fixes those gaps with new detection rules, automatically tunes new rules to suppress false positives, and quickly generates new detections for emerging CVEs to ensure you can quickly detect and contain adversaries’ exploit attempts.

Conductor's joining Meta, so meet Kepler #conductor #softwaredevelopment

If you missed the news, Meta acquired Conductor. If you liked launching multiple coding agents in parallel there, we've got something for you. Kepler ADE by GitKraken lets you run multiple agents in parallel, start sessions straight from a GitHub issue, and keep an eye on them from your phone.

Securing AI Agents Requires More Than a Gateway

Over the past year, I’ve spent a lot of time talking with engineering and platform teams about how they’re deploying AI agents. The conversations are changing. Six months ago, most were focused on getting agents into production. Now, increasingly, the question is how to secure them once they’re there. It’s a familiar transition. We’ve seen it with containers, Kubernetes, microservices, and cloud infrastructure.

Calico on Red Hat OpenShift 5: One Network and Security Model for Containers, VMs and AI

We’re pleased to announce that Calico is supported on Red Hat OpenShift 5, the latest version of the industry’s leading hybrid cloud application platform powered by Kubernetes. Tested and validated to run on Red Hat OpenShift 5, Calico delivers high-performance networking and zero-trust network policy for containers, virtual machines on Red Hat OpenShift Virtualization, and AI workloads, with one consistent policy model across the cluster.

Bindplane's AI Agent is now generally available, plus what else we're bringing to KubeCon NA 2026

KubeCon + CloudNativeCon North America is in Salt Lake City this week, and Bindplane will be at booth 253. Come say hi! We have four talks and we're bringing a ton of cool updates with us. So many of you were eager to try Bindplane Agent while it was in early access. That changes today. Bindplane Agent is generally available. If you've built pipelines in Bindplane before, you know the drill. Pick a source, pick a destination, add processors in the right order, fill in the settings, roll it out.

Rails 8.1.4.1 Is a Big Security Release. Upgrade This Week.

Rails 8.1.4.1 is a security point release, and it’s a substantial one. It carries around a dozen CVE-level advisories spread across Action View, Action Pack, and Active Support. There are no feature changes to weigh and no behavior most apps need to plan around, which makes this the easy kind of upgrade to justify: bump it this week. (The fixes were also backported to the 8.0 and 7.x series, so you don’t have to be on 8.1 to get them.)

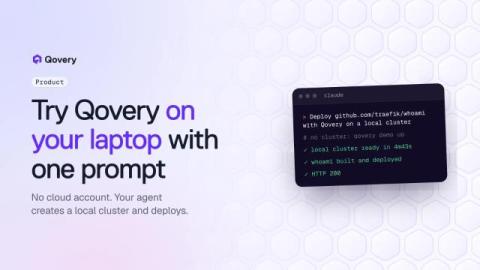
Try Qovery on Your Laptop: Ask Your Coding Agent, Get a Running App

The Qovery agent skills now create a free local Kubernetes cluster in Docker when your organization has none, then deploy your project to it. One prompt in Claude Code, Cursor or OpenCode, no cloud account, no credit card. Measured: 4 min 43 s for the cluster, 2 min 40 s to build and deploy a GitHub repository. Romaric founded Qovery to make Kubernetes accessible to every engineering team. He writes about platform strategy, developer experience, and the future of cloud infrastructure.

How eMudhra, TWCA, and GoDaddy incidents compare against other CAs

Three CAs had very different bad weeks this fall. eMudhra lost a root and quit. GoDaddy had to replace 403,643 certificates over a policy document. TWCA revoked 82% of its certificates over serial numbers. TWCA and eMudhra both failed from a lack of randomness. eMudhra’s private keys had so little that anyone could compute them. TWCA’s CA certificates have serial numbers with 24 random bits where the rules require 64.