Operations | Monitoring | ITSM | DevOps | Cloud

The latest News and Information on CyberSecurity for Applications, Services and Infrastructure, and related technologies.

TryHackMe Alternatives for Blue-Team Training

For IT operations teams moving into defensive security, TryHackMe is a common first stop. Its guided rooms run in the browser, and its SOC Simulator has analysts triage alerts and write case reports in scenarios that can run in Splunk, Elastic or Sentinel. As skills develop, training needs change. You might want longer investigations, a certification that fits a development plan, progress reporting across several analysts or labs that look like your own tooling.
The NSA said wildcard certificates are bad. Everyone uses them anyway.

In October 2021 the NSA published an advisory titled “Avoid Dangers of Wildcard TLS Certificates.” It reiterated what security consultants had been saying for years: don’t use wildcard certificates. Single-name certificates per host are safer. Five years later, we counted the certificates that are actually used. One in three domains has a wildcard on it. For.bank domains, where you need a security review just to register, it’s four in five. Operators aren’t careless.

How Configuration Monitoring Helps Detect Zero-Day Activity

Last updated: October 9, 2026 A zero-day vulnerability may be unknown, but its effects often are not. Exploitation can leave behind observable changes: a new privileged account, an altered management setting, an unexpected file, a modified access rule, or configuration drift from an approved baseline. That makes zero-day configuration monitoring an important part of a defense-in-depth strategy.

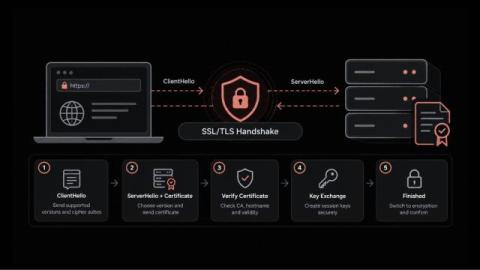
SSL Handshake Guide Covering Each Step and the Fixes That Prevent Outages

Why would a website that passes every uptime check still show customers a security warning? In most cases, the server is running and the network is healthy. The failure happens earlier, during the brief exchange in which the browser and the server agree on how to communicate securely. That moment is the SSL handshake. If it goes wrong, users get an error page while your dashboards stay green. Maybe a certificate expired; maybe a routine change left both sides on different protocol versions.

How to Integrate NinjaOne with a SIEM

In this episode of NinjaOne01, Jeff Hunter, Field CTO at NinjaOne, walks through NinjaOne’s new SIEM Exporter App. The app is a dedicated place to set up and monitor the webhooks that send NinjaOne activity data to your third-party SIEM (Security Information & Event Management) system. Note: this is an early access feature, so contact your account manager to have it enabled for your account. What this video covers.

7 Layers of Agent Security (1 in 6 repos has leaked credentials)

I scanned 10,705 public GitHub repos for leaked credentials. After removing obvious placeholders, 3,543 still had something that looked like a key, and 1,680 held almost 7,000 credentials in recognizable formats like Stripe keys. If you're new to coding with agents (or you've been a dev for decades), this is the setup I'd want you to have before you ship anything public.

How Modern Firewalls Help Businesses Strengthen Network Security

As business networks become more complex, the methods used to attack them are evolving as well. Organisations now need to protect cloud services, remote workers, connected devices, internal applications, and large volumes of data, often across multiple locations. Traditional perimeter security alone is no longer sufficient to address this environment.

Certificate monitoring with TLS, chain, and post-quantum readiness

Most customers start CertKit with SSL host monitoring. On day one, you point CertKit at the systems you already run and get every certificate and when it expires. You start with confidence that you have everything under control. Then, you automate, letting CertKit take over the certificates as they need to be renewed. Each renewal is the last time you ever have to worry about that certificate.

Deutsche Bank leads the way on secure adoption of AI enabled software delivery

As AI accelerates software development and expands its scale, Deutsche Bank is taking a leading role in ensuring the technology can be adopted safely, securely, and responsibly across regulated industries. As an investor, Deutsche Bank’s Corporate Venture Capital arm participated in Kosli’s Series A funding round, reinforcing the bank’s view that automated governance will be a key enabler of AI-assisted software delivery in regulated industries.