Operations | Monitoring | ITSM | DevOps | Cloud

The latest News and Information on CyberSecurity for Applications, Services and Infrastructure, and related technologies.

What's taking DNS-PERSIST-01 so long?

In February, Let’s Encrypt announced that DNS-PERSIST-01 was coming, “some time in Q2 2026.” It’s October, and it’s nowhere close to ready. We’ve been waiting for DNS-PERSIST-01 since January, along with every other ACME client and lots of organizations. DNS-PERSIST-01 promised to simplify domain validation and make automation easier, but we had to wait on Let’s Encrypt. Let’s Encrypt is waiting on a redesign, a standards body, and maybe one more vote.
9 Best AI Penetration Testing Companies for Enterprise Security Teams

Enterprise security teams know the value of penetration testing. The problem is the schedule. A large organization may run hundreds of web applications, thousands of API endpoints, mobile apps, AI features, and a sprawling external attack surface, and much of it changes every week. An annual or quarterly pentest examines a snapshot of that environment, produces a report weeks later, and leaves most of the year untested.

HIPAA Wasn't Written for AI Agents. It Applies to Them Anyway

In short, healthcare is adopting AI agents faster than almost any other industry. More than 85% of Epic’s customers already use Epic AI, Epic’s Agent Factory will let every health system build agents of its own from 2027, and 43% of health systems were piloting agentic AI at the start of this year.

A Simple First-Project Workflow for Trying Seedance 2.5

A first AI video project becomes difficult to evaluate when the idea includes several subjects, changing locations, camera moves, and a detailed story. If the output fails, a beginner may have no clear way to tell what went wrong. A small project gives each revision a useful purpose. Try Seedance 2.5 with one visible action and a simple ending. Treat the first output as a draft to inspect before editing.

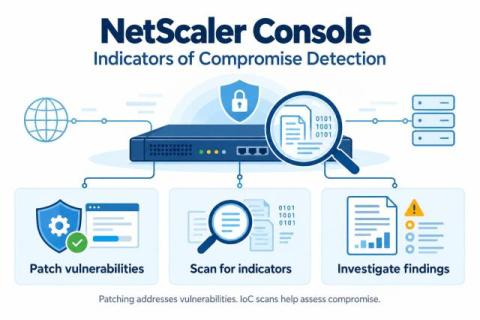
NetScaler Console Indicators of Compromise Detection

On September 27, 2026, Citrix published a security bulletin covering eight new vulnerabilities in NetScaler ADC and NetScaler Gateway. Some of these vulnerabilities are critical and have already been exploited in the wild. Citrix released fixed NetScaler builds and recommends upgrading affected appliances as soon as possible. However, when a vulnerability is already being actively exploited, installing the update only solves part of the problem.

SAST vs SCA vs DAST vs IAST: choosing the right scan for the right stage

SAST vs SCA vs DAST vs IAST: a clear breakdown of what each scan finds, when to run it, and how to combine them across your SDLC. Most AppSec teams don't run one type of scan - they run several, at different points in the pipeline, because no single tool sees the whole picture. This article breaks down SAST vs SCA vs DAST vs IAST: what each one actually tests, where it fits in the software development lifecycle (SDLC), and how to combine them without duplicating effort or drowning developers in findings.

What is Interactive Application Security Testing (IAST)?

Interactive Application Security Testing (IAST) finds vulnerabilities in running applications by monitoring code from the inside. Learn how it works and where it fits. Interactive Application Security Testing (IAST) is a method for finding security vulnerabilities in an application while it's running, by instrumenting the code and observing how it behaves during normal use or testing.