Operations | Monitoring | ITSM | DevOps | Cloud

The latest News and Information on CyberSecurity for Applications, Services and Infrastructure, and related technologies.

Top 8 Red Teaming Companies for 2026

Red teaming has become one of the most important ways for security leaders to validate whether their defenses can withstand realistic adversary behavior. Traditional vulnerability scans and annual penetr ation tests still matter, but they do not always show how attackers move across identity systems, cloud environments, endpoints, applications, networks, and people-driven processes. A strong red teaming company helps an organization answer a harder question: can our security program detect, contain, and respond to a realistic attack before real damage occurs?
Sponsored Post

5 Ways to Use Log Analytics and Telemetry Data for Fraud Prevention

As fraud continues to grow in prevalence, SecOps teams are increasingly investing in fraud prevention capabilities to protect themselves and their customers. One approach that's proved reliable is the use of log analytics and telemetry data for fraud prevention. By collecting and analyzing data from various sources, including server logs, network traffic, and user behavior, enterprise SecOps teams can identify patterns and anomalies in real time that may indicate fraudulent activity.

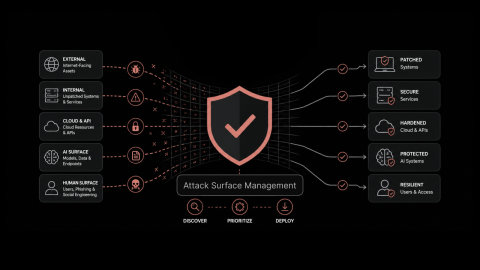
What Is Attack Surface Management and How Does Patching Reduce It?

Your exposure list grows faster than your team can clear it. Security adds new findings every week, and your IT team gets to a fraction of them. Everything left over is a backlog an attacker can walk straight through, and buying another scanner will not shrink it. Most attack surface management programs live inside that gap. Finding exposures got easy. Closing them did not, and a queue nobody has time to work is where the risk quietly builds.

Why Every Modern Security Operation Center Needs Automation and AI

Security teams no longer face a simple monitoring problem. In most cases, they face - While cloud workloads change by the minute, identities move across applications. In general, endpoints appear outside the traditional perimeter. Meanwhile, the modern security operations center must interpret all that activity. It must also not let a genuine threat disappear inside routine noise. Although traditional processes still matter, manual triage cannot carry the entire workload anymore. In fact, analysts lose valuable investigation time if they -

CertKit Private PKI: A private certificate authority without running one yourself

In May I wrote that you probably don’t need private PKI for internal infrastructure, because DNS validation gets a publicly trusted certificate onto hosts that never touch the internet. In June I pointed out that Apple enforces an 825-day cap on private certificates, so your own CA doesn’t even free you from the browser vendors. Two days ago I told you that public client certificates stop renewing in October, and that the replacement is a private certificate authority.

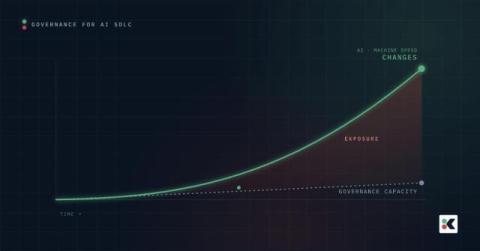
Agent Guard: Control AI Assets Before They Become Shadow AI

A developer on your team just told Claude Code to connect to a new MCP server, the protocol coding agents use to reach organizational tools and data. Nobody in security reviewed it. Nobody in security even knows it happened. For two-thirds of enterprises, the primary obstacle to scaling agentic development isn’t budget or headcount — it’s security risk.