Operations | Monitoring | ITSM | DevOps | Cloud

The latest News and Information on CyberSecurity for Applications, Services and Infrastructure, and related technologies.

Supply chain hit: the first hours are about "am I affected?"

The first two to three hours after a supply chain compromise aren't about remediation – they're about figuring out whether you're affected at all. That requires two things: a feed of compromised packages you can cross-reference against what you're using, and an audit trail showing which developers pulled which packages and when. Teams that can answer "are we affected?" in 30 minutes have that data pre-built into their platform. Teams that don't are still piecing it together at hour three. Protect your supply chain with Cloudsmith.
Tier 1 SOC Automation Options Explained

In 2026, like in every other year, tier 1 is the front line of the SOC. It's where alerts land, where triage happens, and where most of the repetitive work lives. Unsurprisingly, it is also where automation is moving fastest. There is a lot of skepticism around how much of tier 1 can be reliably automated. If you want to see some, just have a look on Reddit or other forums. But there is definitely a growing market and capability for AI-enabled tools to learn, guide and automate tier 1 workflows.

How Network on Chip Encryption Protects Sensitive Data Between Processing Elements

Modern systems on chip combine multiple processors, memory controllers and hardware components into one device. Because these parts exchange large volumes of information, the security of internal communication is a primary concern for the system. Using encryption within the communication fabric is a method to lower the risk that unauthorized parties will access data while it moves between components.

How Claude Mythos Changes the Future of Vulnerability Management: Fixing, Not Finding

Anthropic’s Claude Mythos shows how AI is making vulnerability discovery nearly infinite. Endpoint remediation is where IT teams win or lose. In April 2026, Anthropic introduced Claude Mythos Preview, an AI model that autonomously discovered thousands of previously unknown vulnerabilities across every major operating system and web browser. By late May, the running total had passed 23,000 potential findings, and the vast majority were still unpatched.

Migrate First, Modernize Later: A Leadership Guide to Converging VMs and Containers to Run AI Workloads

Every so often the ground under enterprise IT moves. It’s moving now. Across industries, organizations are consolidating fragmented infrastructure onto a single, self-hosted platform capable of running both containers and virtual machines side by side. The motivation is simple: simplify operations, lower cost and reallocate resources & budget to AI initiatives. Kubernetes is emerging as the primary platform for many of these workloads.

The secure path should be the default path - nothing more

Asking developers to take extra steps to pull securely is a policy that won't hold. The only approach that scales is making the private registry the default – a buffer between the developer and public registries that applies policy automatically at the global level. No extra steps, no security theater, no cognitive overhead at the point of pull. Automation and global policy configuration are what turn good intentions into a default secure posture.

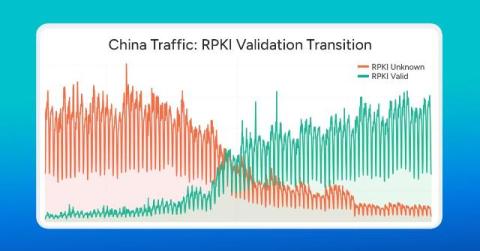
China Rolls out the ROAs

Long a laggard in RPKI adoption, China has dramatically increased its ROA coverage from 4% to 81% since April, signaling a major commitment to securing the internet’s routing system. This post explores the dramatic shift marking a significant milestone in global routing security, helping to protect networks from BGP routing mishaps that cause internet disruptions.

What Happens to a VM's IP When It Moves During Migration?

A KubeVirt VM runs inside a pod. That is the trick that lets Kubernetes schedule a VM like any other workload. It also means the VM and the pod have different lifecycles. The VM is long-lived and has a stable identity. The pod is disposable. When the VM reboots, gets evicted, or live-migrates, the pod underneath is destroyed and a new one is created.

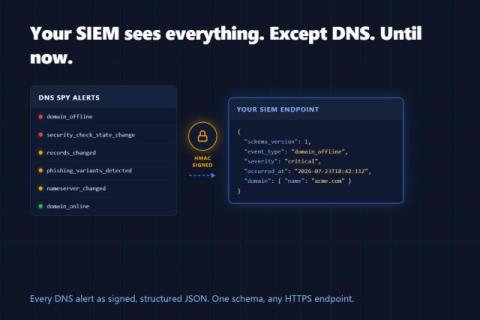
Send DNS Spy Alerts to Your SIEM: Introducing Webhook Alerts

Enterprise teams can now add a Webhook alert channel that POSTs every DNS Spy alert — DNS record changes, domain outages, security check failures, WHOIS updates, phishing look-alike detections — to any HTTPS endpoint as structured JSON. Requests are optionally HMAC-signed, every delivery is logged and retried, and a Send Test button verifies your integration end to end.