Operations | Monitoring | ITSM | DevOps | Cloud

AI Finds and Fixes Security Vulnerabilities | Harness Demo

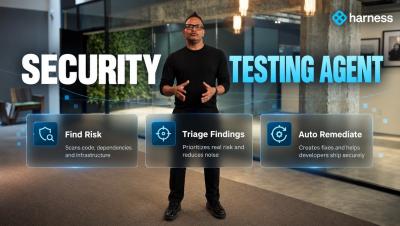
What if AI could find a security vulnerability, determine whether it actually matters, write the fix, validate it, and open a pull request for review? In this demo, see how Harness Security Testing Agents work together to move from vulnerability detection to a verified fix with an audit trail along the way. The system uses three agents: Harness can analyze where vulnerabilities exist in your environment, determine whether they’re actually reachable, prioritize what needs to be fixed, and automatically create remediation pull requests.
The Five Levels of the Enterprise AI Software Factory

Scroll LinkedIn for ten minutes and you'd think every engineering organization already runs an autonomous SDLC, with agents writing, reviewing, and shipping code while humans watch. Inside large enterprises, the picture looks different. Coding agents there have to work around sensitive customer data, recurring compliance audits, a larger attack surface, downtime that costs millions, and a CFO who wants to know what last year's token spend bought.

Debug Production at the Speed of AI

Your coding agent can debug production issues now. Yes… Not just “help you debug.” Actually run the investigation… FOR YOU! In this new era of agentic development, speed matters. And in the old days (you know… last week or so) we used to investigate production bugs ourselves. Manually. Like humans. But for a lot of incidents, we don’t need to do all of that anymore.

Harness acquires Augment Code to advance the Autonomous SDLC

Harness Cosmos Software Factory Agent automates engineering from idea to code, connecting code context with delivery, security, testing, and production workflows. The world runs on software. Better healthcare, more accessible financial services, more efficient businesses, and better everyday experiences all depend on our ability to build and improve it. AI is making that faster, but the outcome that matters is not simply how much code we generate.

How we investigate Sentry errors with an AI agent

We built an AI agent on Qovery to investigate Sentry alerts before our team picks them up. Here’s how the workflow runs, what it delivers, and where engineers still need to step in. Rémi is a staff frontend engineer at Qovery. He writes about frontend architecture, developer experience, and building scalable UI systems for platform engineering tools.

Building AI SRE Agents, Part 3: Autonomous in the Cloud

Your agent has earned trust in shadow mode. Now it runs on its own: an alert fires, the agent starts, investigates and proposes a fix before anyone opens a laptop. Here is what it takes to make that safe, scalable and better every week. This is the third article in a series on taking an AI SRE agent from a weekend experiment to production. Part 1 built a local, read-only agent on a throwaway cluster and refined it against a synthetic eval set.

Where Jev fits in ops

If you're using agents and MCPs to get a better understanding of your environment or work through an investigation, you can get a lot of useful information back. You can pull logs, look at recent changes, and check how services are configured, but you're still the one deciding what to do with all of it. That part of the process still lives in your head. To see where Jev might fit, look at decisions your team already makes and work backwards from them.

10 Best AI Agent Infrastructure Platforms in 2026

AI agent infrastructure is the set of platforms that run agents and the code they write. It has three layers: sandboxes that isolate untrusted, model-generated code, runtimes that run the agent and its services in production, and orchestration layers that save an agent’s progress so a long run can resume after a failure. Most production agents need more than one layer. This guide compares 10 platforms across all three, with isolation, state, deployment, and compliance for each.